The data platform for
security, observability, and AI
Bring scattered machine data together to stop threats faster and prevent downtime before it happens.
About Splunk
Splunk is a data platform that collects and analyzes all of your machine data — logs, events, metrics, and more. Security teams use it to detect and respond to threats, while IT operations teams use the same data to find root causes and keep services running.
Acquired by Cisco in 2024, it is now offered as Splunk by Cisco alongside Cisco security and networking products.
All your data in one place
Work with security, observability, and network data on one platform. Search data right where it lives, without moving it, to keep costs down.
Faster threat response
Pick out real threats from a flood of security alerts and automate repetitive response work so your security team can move faster.
Prevent downtime
See infrastructure and application health in real time, and find and fix root causes before users are affected.
AI built for security and observability
AI agents and assistants predict issues, cut repetitive work, and speed up resolution. You can also observe and manage the AI agents and models your organization has deployed.
Connects directly to Cisco security and network data
Logs and alerts from Cisco security products flow into Splunk through a single Cisco Security Cloud app, and network path performance data connects to Splunk Observability. If you already use Cisco, you can analyze it all in Splunk without custom development.
and responds to XDR incidents too
Key products and solutions
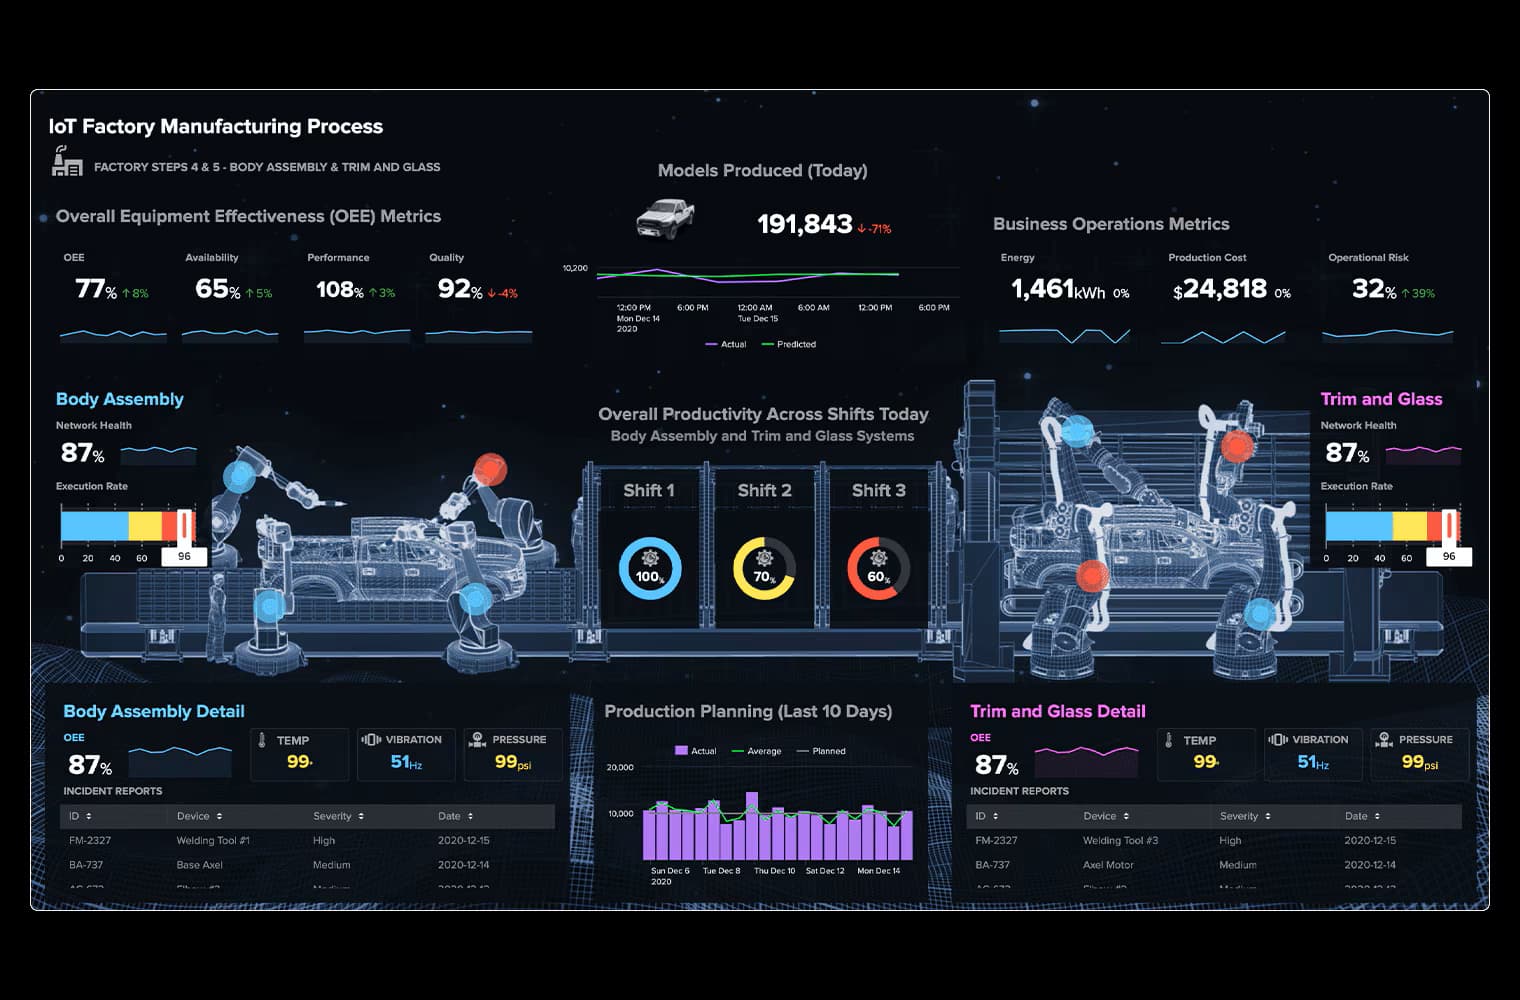
Splunk Cloud Platform
The Splunk data platform delivered as a cloud service. Collect, search, and analyze all your machine data without managing servers.
Learn more at Splunk →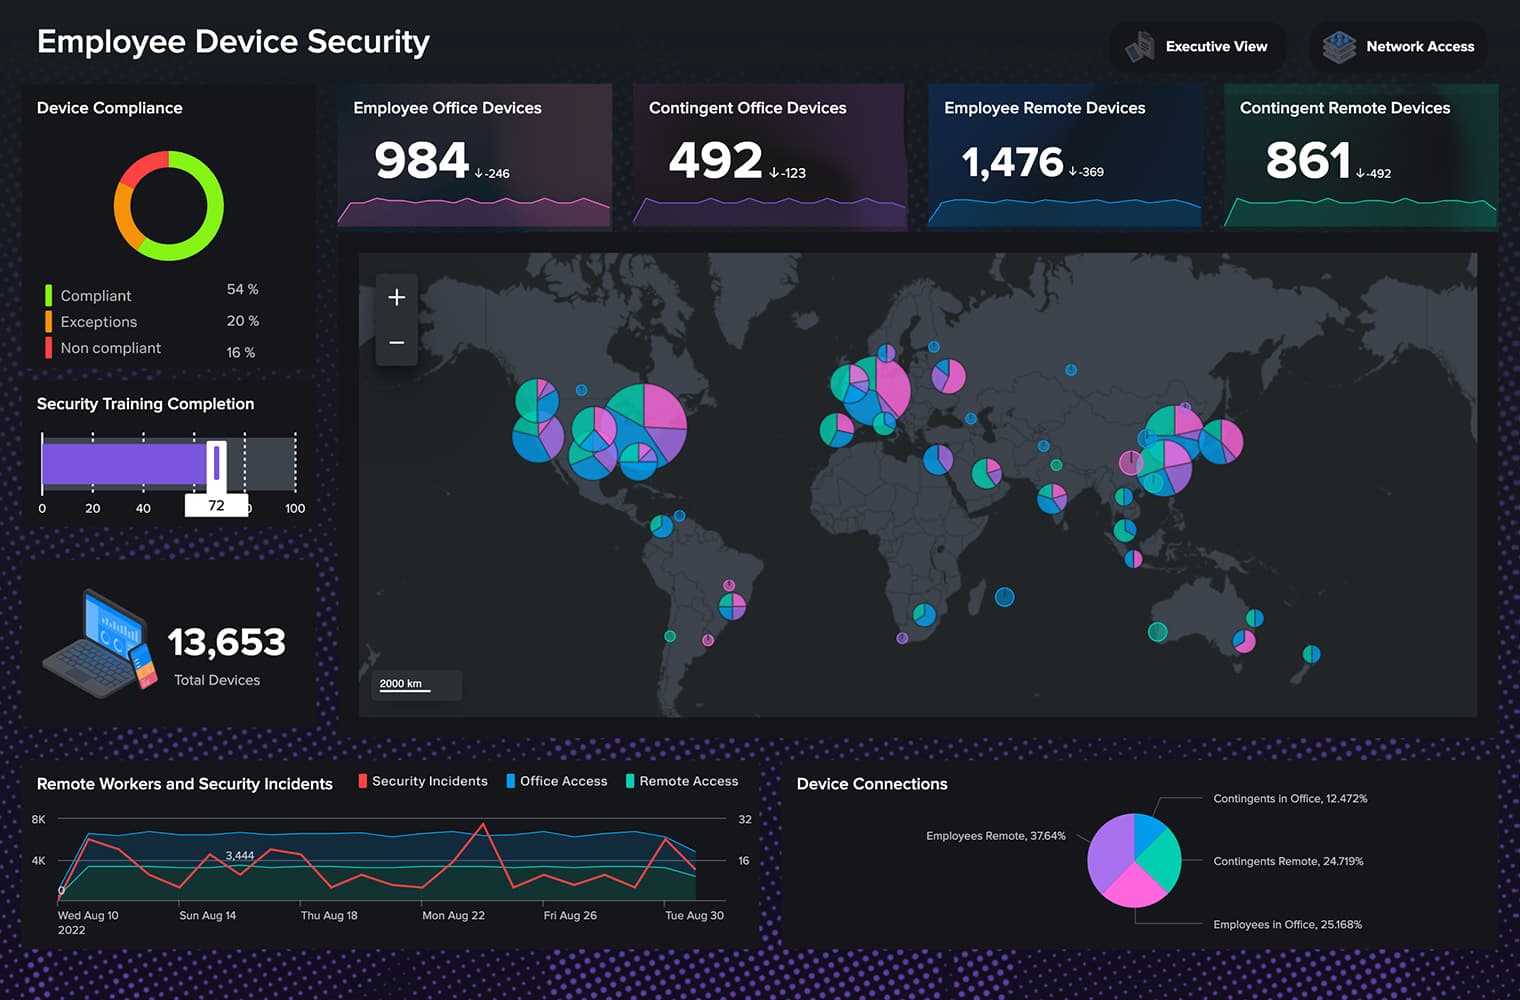
Splunk Enterprise
The Splunk data platform you deploy and run yourself — on-premises, in a private cloud, or in hybrid environments.
Learn more at Splunk →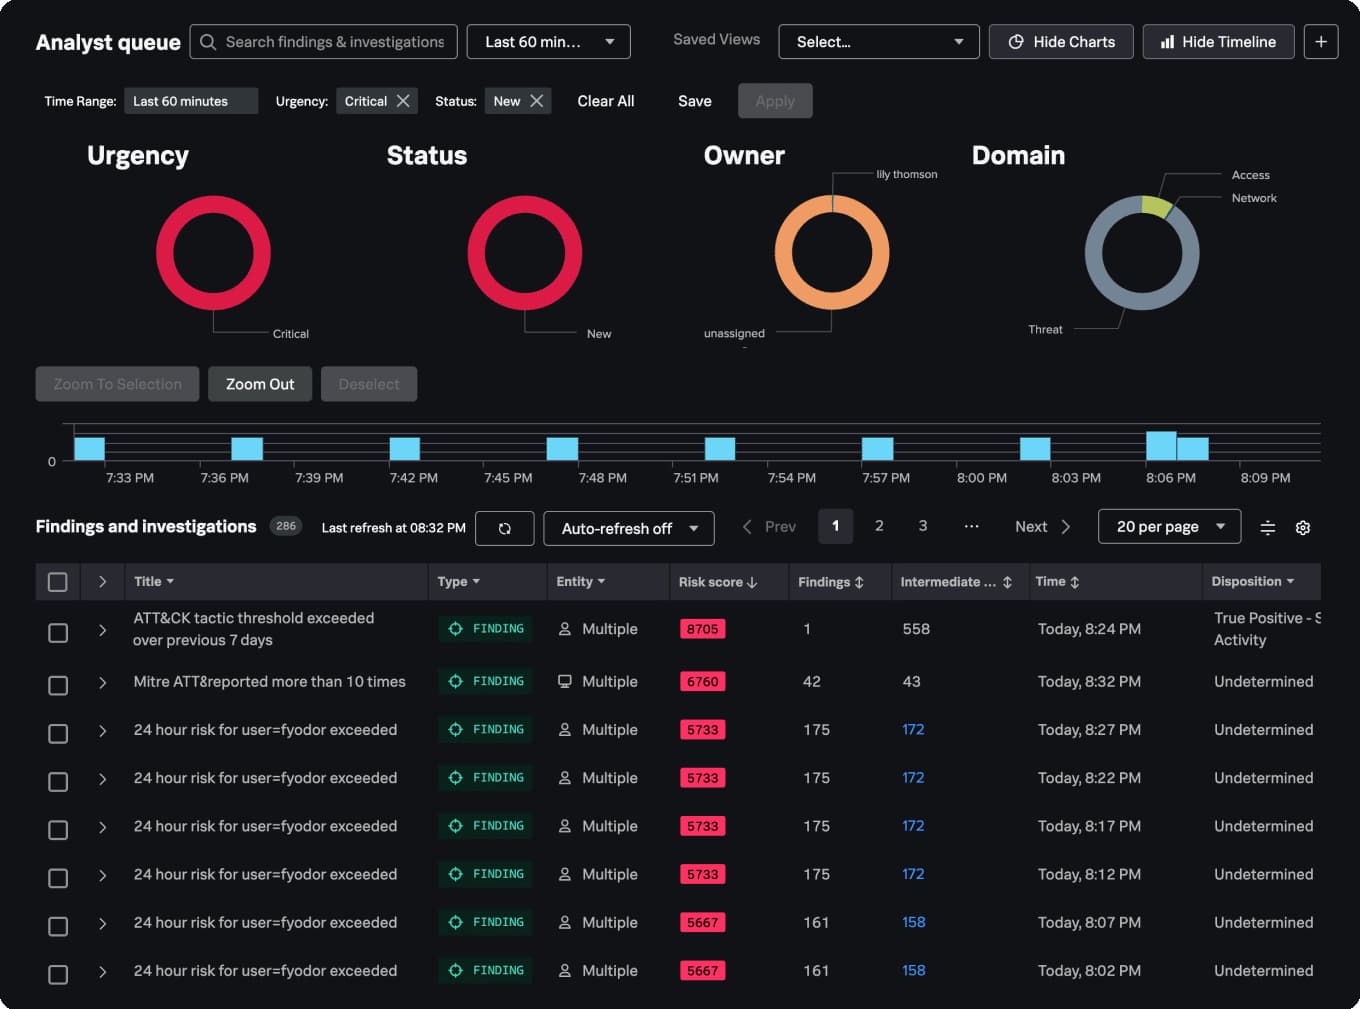
Splunk Enterprise Security
An AI-powered security operations platform that unifies threat detection, investigation, and response. Includes SIEM, response automation (SOAR), and behavior analytics (UEBA).
Learn more at Splunk →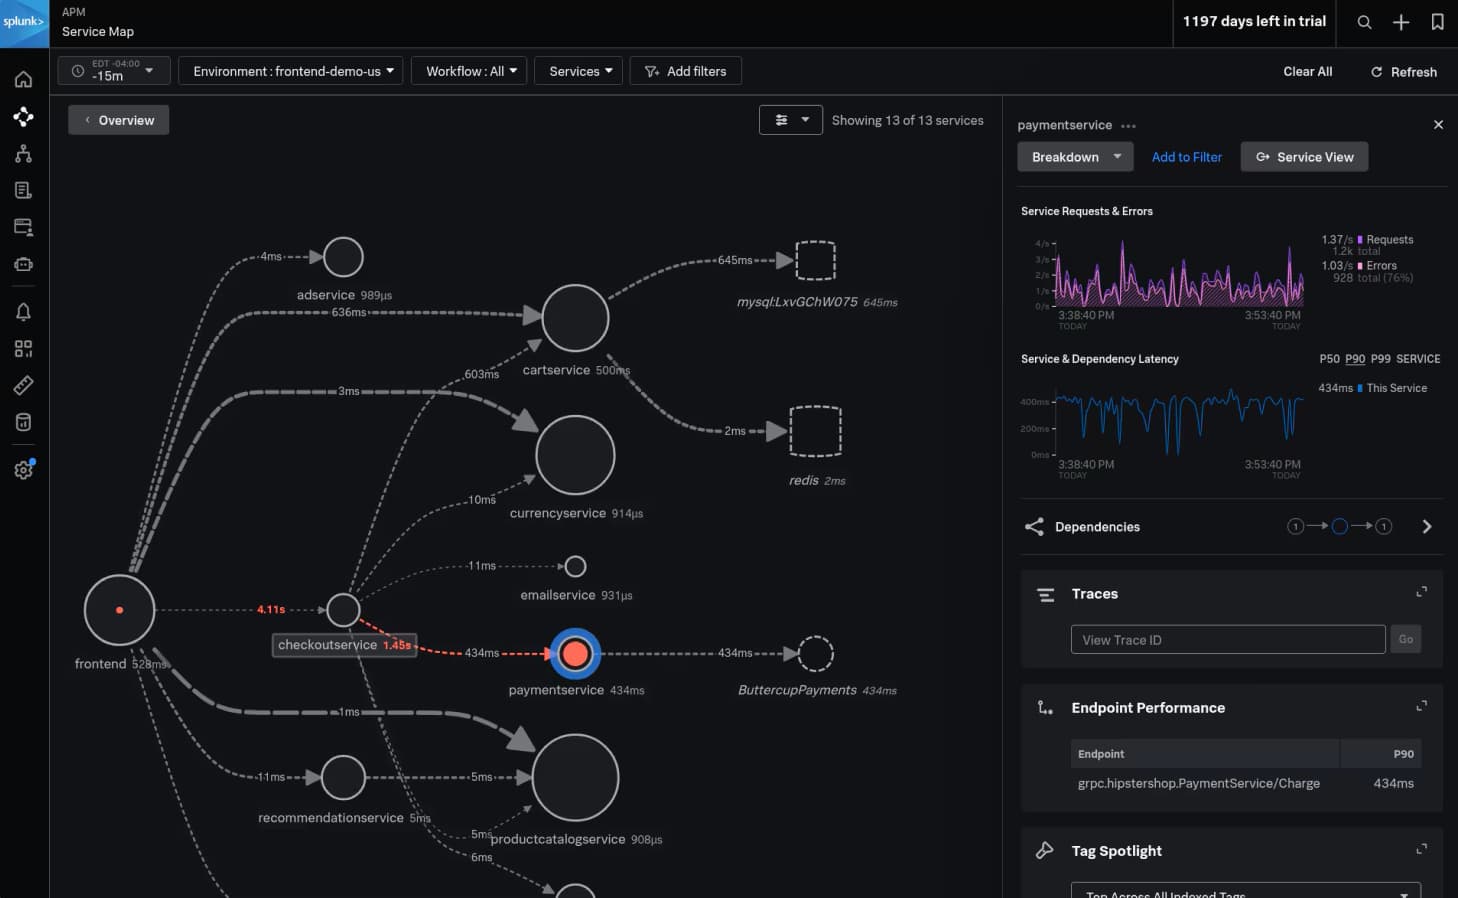
Splunk Observability Cloud
Monitors infrastructure and application performance in real time across cloud, container, and on-premises environments, and pinpoints root causes.
Learn more at Splunk →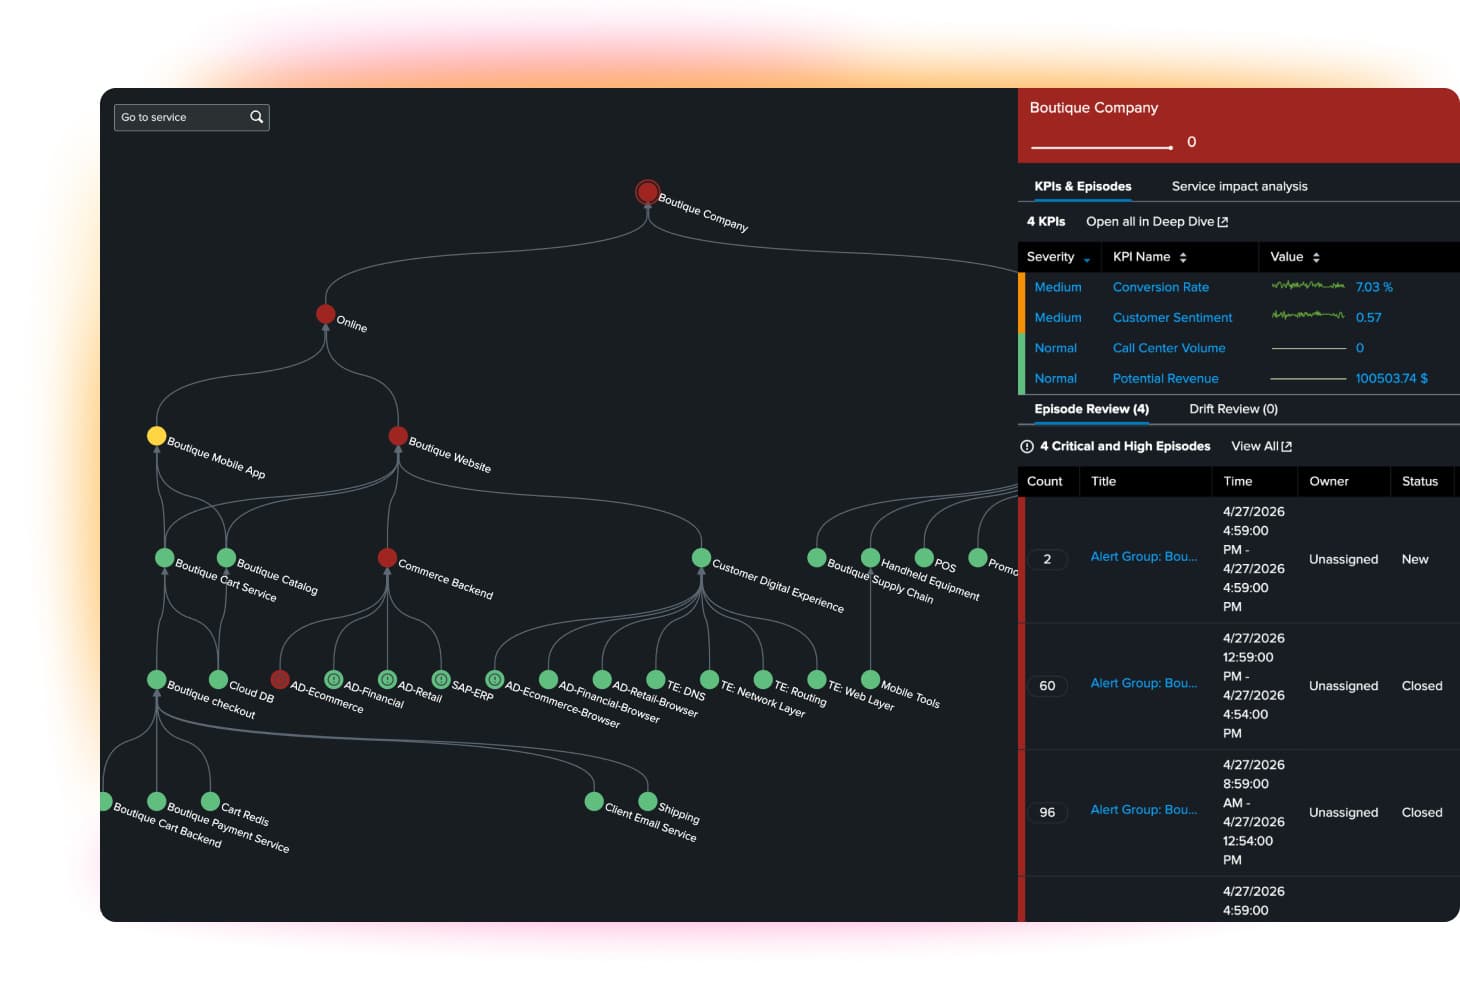
Splunk IT Service Intelligence
Uses AIOps to show business service health in a single view and catch degradation early to protect your services.
Learn more at Splunk →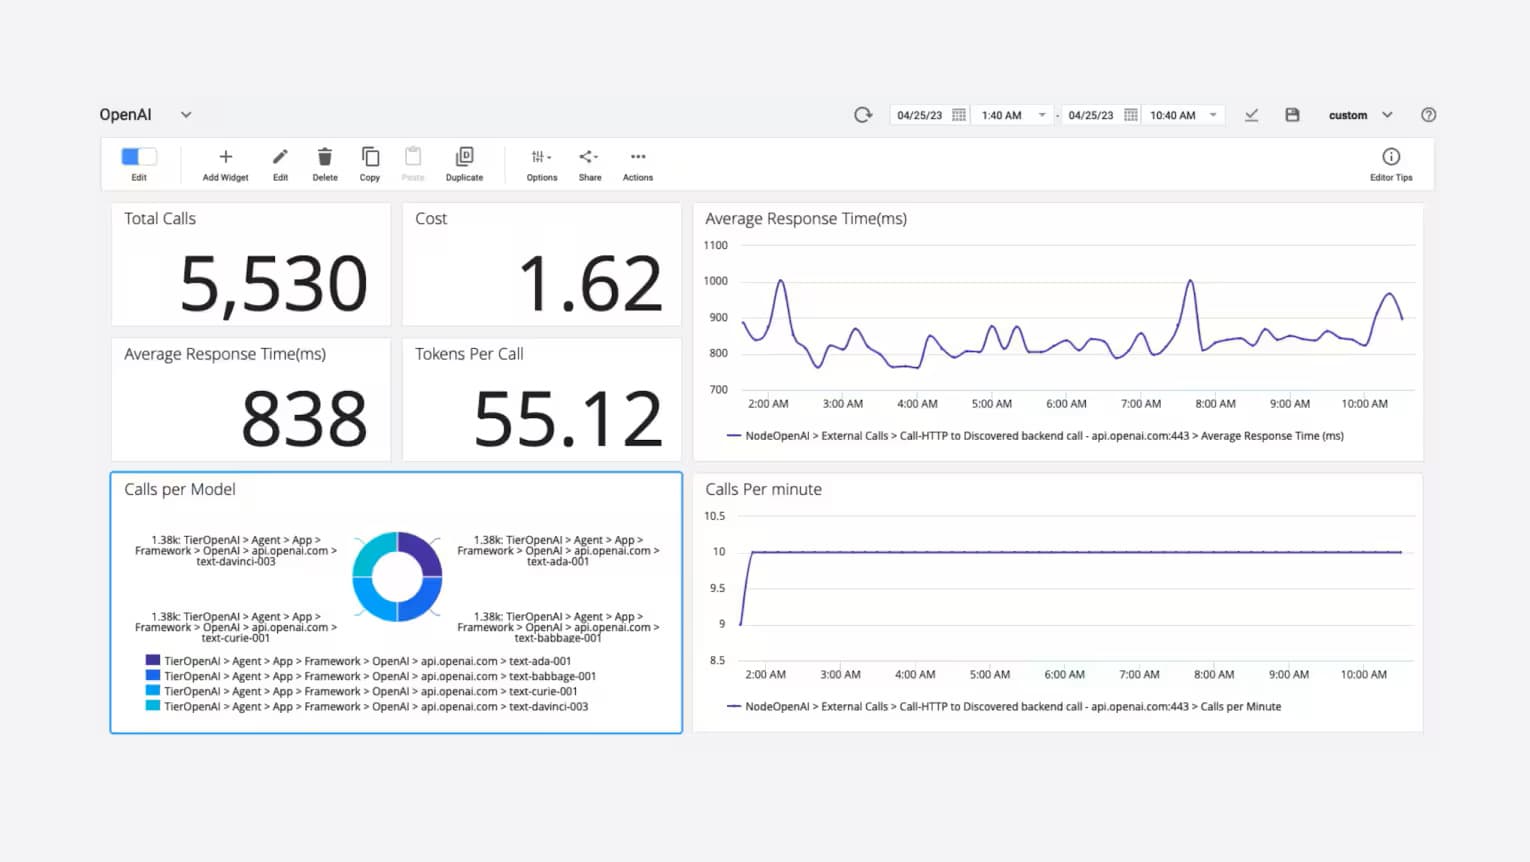
Splunk AppDynamics
Traces application performance across the full stack, showing both why things slowed down and the business impact.
Learn more at Splunk →
For sales, technical support, training, or vendor contract inquiries, please use the button below to contact us.
Submit your inquiry through the form, and a member of our team will review it and respond to you promptly.

Image Courtesy : Splunk LLC, a Cisco company. All rights reserved.